
8. AP Tab
8.1. AP
Use the controls on the AP tab to set the wireless SSID, AP settings and Mesh, as well as wireless distribution system (WDS) settings.
8.1.1. Wireless SSID
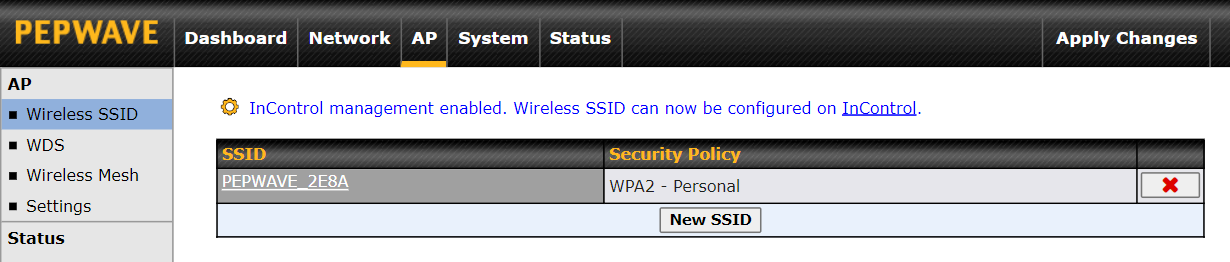
Wireless network settings, including the name of the network (SSID) and security policy, can be defined and managed in this section.
Click New SSID to create a new network profile, or click the existing network profile to modify its settings.
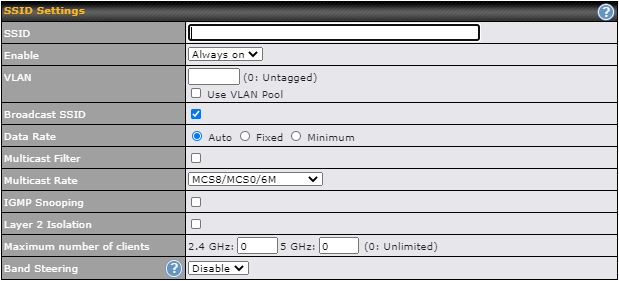
SSID Settings | |
SSID | This setting specifies the router’s SSID that Wi-Fi clients will see when scanning for Wi-Fi signals. |
Enable | Click the drop-down menu to choose predefined schedules as your starting point. Please note that upon selection, previous changes on the schedule map will be deleted. |
VLAN | This setting specifies the VLAN ID to be tagged on all outgoing packets generated from this wireless network (i.e. packets that travel from the Wi-Fi segment through your access point to the ethernet segment via the LAN port). If 802.1x is enabled and a per-user VLAN ID is specified in the authentication reply from the RADIUS server, then the value specified by the default VLAN ID will be overridden. The default value of this setting is 0, which means that VLAN tagging is disabled (instead of tagged with zero). If Use VLAN Pool is enabled, enter the VLAN pool value specified in VLAN. |
Broadcast SSID | This setting specifies whether or not Wi-Fi clients can scan the SSID of this wireless network. Broadcast SSID is enabled by default. |
Data Rate | Select Auto to allow your access point to set the data rate automatically, or select Fixed or Minimum to choose a set rate from a drop-down menu. |
Multicast Filter | This setting enables the filtering of multicast network traffic to the wireless SSID. |
Multicast Rate | This setting specifies the transmit rate to be used for sending multicast network traffic. |
IGMP Snooping | To allow your access point to convert multicast traffic to unicast traffic for associated clients, select this option. |
Layer 2 Isolation | Layer 2 refers to the second layer in the ISO Open System Interconnect model. When this option is enabled, it will block communication between Wi-Fi clients within the same VLAN, SSID or subnet, as a security measure that best suits a company Guest/Visitor Wi-Fi access scenario. Do refer to this link (https://forum.peplink.com/t/lan-isolation-with-balance30-and-ap-one-ac-minihelp-needed/3914/4) for visual illustration of the feature. By default, the setting is disabled. |
Maximum Number of Clients | Enter the maximum number of clients that can simultaneously connect to your access point, or enter 0 to allow unlimited Wi-Fi clients. |
Band Steering | This setting, shown below, allows you to reduce 2.4 GHz band overcrowding, AP with band steering steers clients capable of 5 GHz operation to 5 GHz frequency. Force - Clients capable of 5 GHz operation are only offered with 5 GHz frequency.
|


Security Settings | |
Security Policy | This setting configures the wireless authentication and encryption methods. Available options are:
To allow any Wi-Fi client to access your AP without authentication, select Open (No Encryption). Details on each of the available authentication methods follow. |
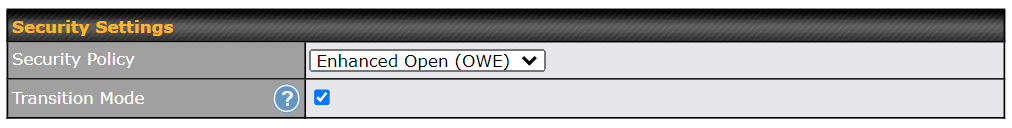
Enhanced Open (OWE) | |
Transition Mode | With the option enabled, legacy clients will be able to connect in Open mode. With the option disabled, legacy clients will not be able to connect. OWE-supported clients will always connect in OWE mode. |
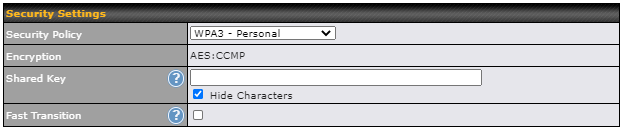
WPA3 – Personal | |
Shared Key | Enter a passphrase of between 8 and 63 alphanumeric characters to create a passphrase used for data encryption and authentication. Click Hide / Show Characters to toggle visibility. |
Fast Transition | Fast Transition |
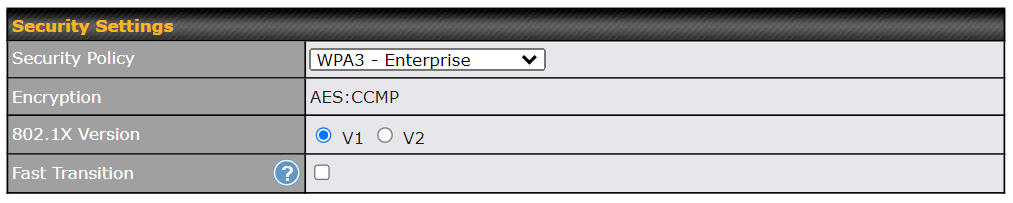
WPA3 – Enterprise | |
802.1X Version | Choose v1 or v2 of the 802.1x EAPOL. When v1 is selected, both v1 and v2 clients can associate with the access point. When v2 is selected, only v2 clients can associate with the access point. Most modern wireless clients support v2. For stations that do not support v2, select v1. The default is v2. |
Fast Transition | Fast Transition |
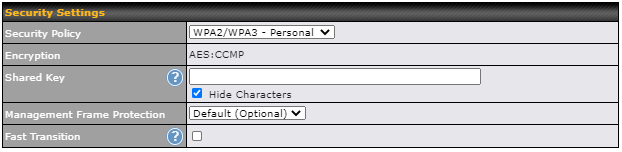
WPA2/WPA3 – Personal | |
Shared Key | Enter a passphrase of between 8 and 63 alphanumeric characters to create a passphrase used for data encryption and authentication. Click Hide / Show Characters to toggle visibility. |
Management Frame Protection | This feature protects stations against forged management frames spoofed from other devices. Frames that are protected include Disassociation, Deauthentication and QoS Action. |
Fast Transition | Fast Transition |
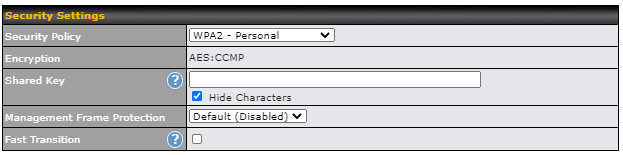
WPA2 – Personal | |
Shared Key | Enter a passphrase of between 8 and 63 alphanumeric characters to create a passphrase used for data encryption and authentication. Click Hide / Show Characters to toggle visibility. |
Management Frame Protection | This feature protects stations against forged management frames spoofed from other devices. Frames that are protected include Disassociation, Deauthentication and QoS Action. |
Fast Transition | Fast Transition |
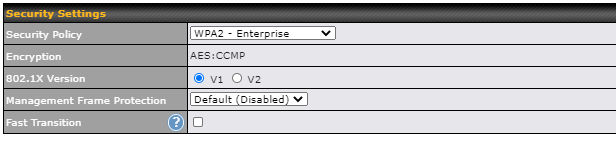
WPA2 – Enterprise | |
802.1X Version | Choose v1 or v2 of the 802.1x EAPOL. When v1 is selected, both v1 and v2 clients can associate with the access point. When v2 is selected, only v2 clients can associate with the access point. Most modern wireless clients support v2. For stations that do not support v2, select v1. The default is v2. |
Management Frame Protection | This feature protects stations against forged management frames spoofed from other devices. Frames that are protected include Disassociation, Deauthentication and QoS Action. |
Fast Transition | Fast Transition |
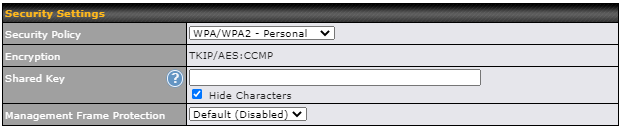
WPA/WPA2 – Personal | |
Shared Key | Enter a passphrase of between 8 and 63 alphanumeric characters to create a passphrase used for data encryption and authentication. Click Hide / Show Characters to toggle visibility. |
Management Frame Protection | This feature protects stations against forged management frames spoofed from other devices. Frames that are protected include Disassociation, Deauthentication and QoS Action. |
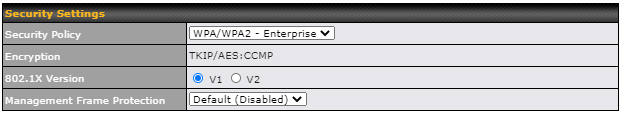
WPA/WPA2 – Enterprise | |
802.1X Version | Choose v1 or v2 of the 802.1x EAPOL. When v1 is selected, both v1 and v2 clients can associate with the access point. When v2 is selected, only v2 clients can associate with the access point. Most modern wireless clients support v2. For stations that do not support v2, select v1. The default is v2. |
Management Frame Protection | This feature protects stations against forged management frames spoofed from other devices. Frames that are protected include Disassociation, Deauthentication and QoS Action. |
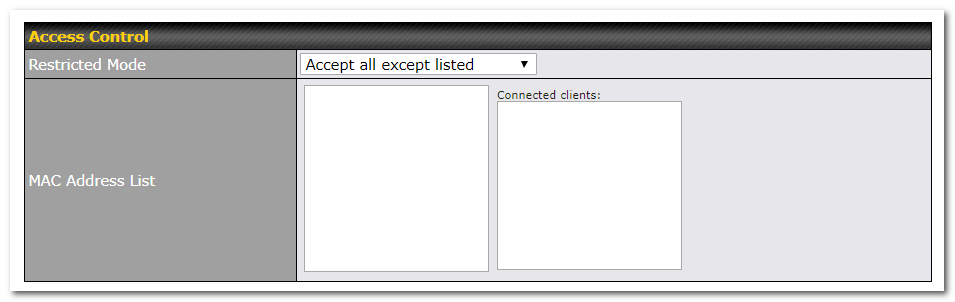
Access Control | |
Restricted Mode | The settings allow the administrator to control access using MAC address filtering. Available options are None, Deny all except listed, Accept all except listed, and RADIUS MAC Authentication. |
MAC Address List | Connections coming from the MAC addresses in this list will be either denied or accepted based on the option selected in the previous field. |
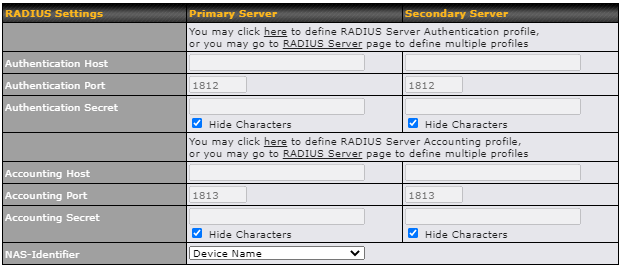
RADIUS Server Settings | |
Host | Enter the IP address of the primary RADIUS server and, if applicable, the secondary RADIUS server. |
Secret | Enter the RADIUS shared secret for the primary server and, if applicable, the secondary RADIUS server. |
Authentication Port | Enter the UDP authentication port(s) used by your RADIUS server(s) or click the Default button to enter 1812. |
Accounting Port | Enter the UDP accounting port(s) used by your RADIUS server(s) or click the Default button to enter 1813. |
NAS-Identifier | Information added to access requests to identify the NAS. |
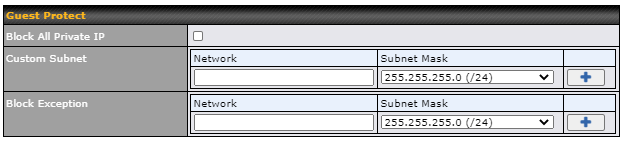
Guest Protect | |
Block All Private IP | Check this box to block access from the Private IP. |
Custom Subnet | To specify a subnet to block, enter the IP address and choose a subnet mask from the drop-down menu. To add the blocked subnet, click |
Block Exception | To create an exception to a blocked subnet (above), enter the IP address and choose a subnet mask from the drop-down menu. To add the exception, click |
 . To delete a blocked subnet, click
 .
 . To delete an exception, click
 .
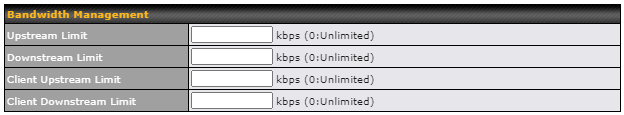
Bandwidth Management | |
Upstream Limit | Enter a value in kbps to limit the wireless network’s upstream bandwidth. Enter 0 to allow unlimited upstream bandwidth. |
Downstream Limit | Enter a value in kbps to limit the wireless network’s downstream bandwidth. Enter 0 to allow unlimited downstream bandwidth. |
Client Upstream Limit | Enter a value in kbps to limit connected clients’ upstream bandwidth. Enter 0 to allow unlimited upstream bandwidth. |
Client Downstream Limit | Enter a value in kbps to limit connected clients’ downstream bandwidth. Enter 0 to allow unlimited downstream bandwidth. |
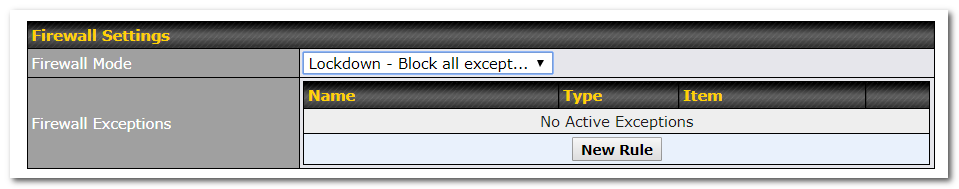
Firewall Settings | |
Firewall Mode | Choose Flexible – Allow all except… or Lockdown – Block all except… to turn on the firewall, then create rules for the firewall exceptions by clicking |
 . See the discussion below for details on creating a firewall rule. To delete a rule, click the associated
 button. To turn off the firewall, select Disable.
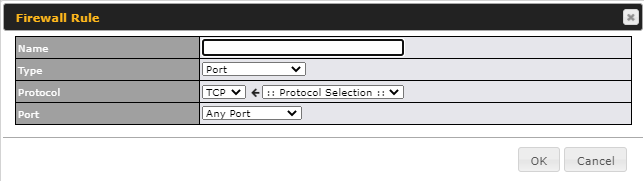
Firewall Rule | |
Name | Enter a descriptive name for the firewall rule in this field. |
Type | Choose Port, IP Network, MAC Address or Domain Name to allow or deny traffic from any of those identifiers. Depending on the option chosen, the following fields will vary. |
Port | Choose TCP or UDP from the Protocol drop-down menu to allow or deny traffic using either of those protocols. From the Port drop-down menu, choose Any Port to allow or deny TCP or UDP traffic on any port. Choose Single Port and then enter a port number in the provided field to allow or block TCP or UDP traffic from that port only. You can also choose Port Range and enter a range of ports in the provided fields to allow or deny TCP or UDP traffic from the specified port range. |
IP Network | If you have chosen IP Network as your firewall rule type, enter the IP address and subnet mask identifying the subnet to allow or deny. |
MAC Address | If you have chosen MAC Address as your firewall rule type, enter the MAC address identifying the machine to allow or deny. |
Domain Name | If you have chosen Domain Name as your firewall rule type, enter the Domain Name identifying the machine to allow or deny. |
8.1.2. Wireless Mesh
Mesh support enables an access point (AP) to connect wirelessly to other wired mesh APs, providing redundancy in the event of AP failure. Mesh support is available for Wi-Fi networks 802.11ac (Wi-Fi 5) and above.
Please note that the AP’s Mesh settings need to match the Mesh ID and Shared Key of the selected frequency band in order for the AP to join the network.
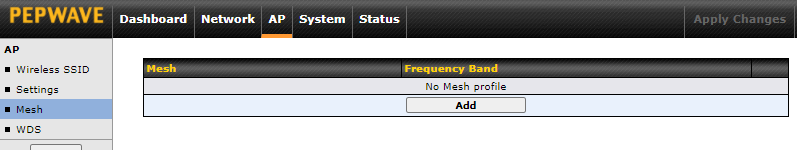
To create a new Wireless Mesh profile, go to AP > Mesh, and click Add.
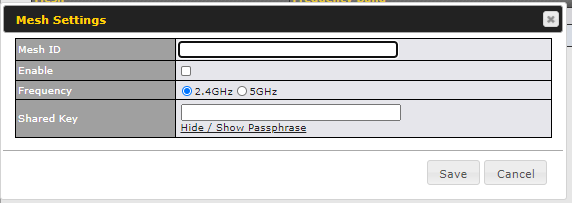
Mesh Settings | |
Mesh ID | Enter a name to represent the Mesh profile. |
Enable | Check the box to enable the Mesh Profile. |
Frequency | Select the 2.4GHz or 5GHz frequency to be used. |
Shared Key | Enter the shared key in the text field. Please note that it needs to match the shared keys of the other APs in the Mesh. Click Hide / Show Passphrase to toggle visibility. |
8.1.3. WDS
A wireless distribution system (WDS) provides a way to link access points together when wired or cabled connections are not feasible or desirable. A WDS can also extend wireless network coverage for wireless clients. Please note that your access point’s channel setting should not be set to Auto when using WDS.
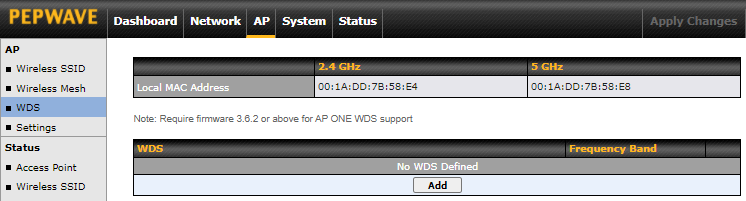
To create a new WDS, go to AP > WDS, and click Add.
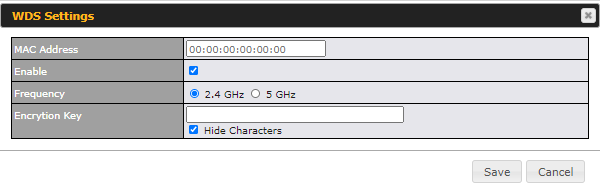
WDS | |
MAC Address | Enter the MAC address of the access point with which to form a WDS link. |
Enable | Check this box to enable WDS. |
Frequency | Select the frequency (2.4GHz or 5GHz) for WDS peer connection. |
Encryption | Select AES to enable encryption for WDS peer connections. Selecting None disables encryption. |
8.1.4. Settings
Basic access point operation settings, such as the protocol and channels used, as well as scanning intervals and other advanced settings can be defined and managed in this section.
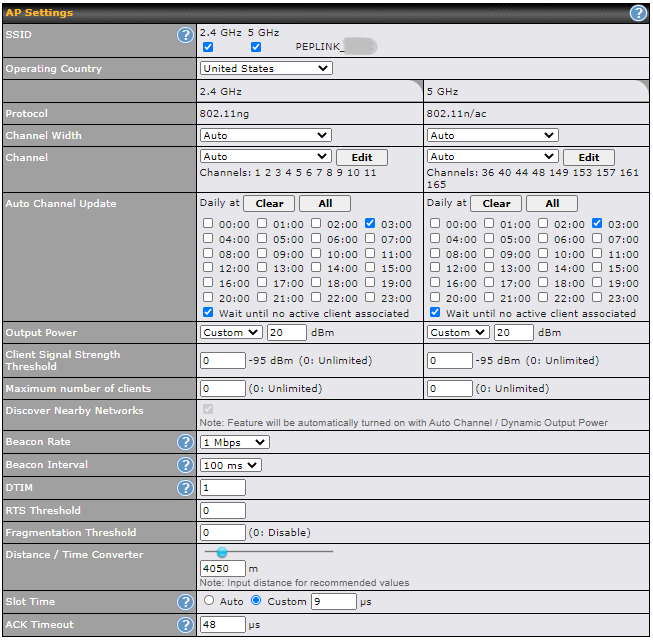
AP Settings | |
SSID | Select if an SSID is broadcasting on 2.4 GHz, 5 GHz or both bands. |
Operating Country | This drop-down menu specifies the national / regional regulations the AP should follow.
|
Protocol | Choose 802.11ng or 802.11n/ac as your access point’s Wi-Fi protocol. The AP One Mini provides the 802.11ng protocol for the 2.4 GHz band and the 802.11n/ac protocol for the 5GHz band, as shown below. |
Channel Width | This option defines which channel width the radio will use: |
Channel | This drop-down menu selects the 2.4 GHz and 5GHz 802.11 channels to be used. When Auto is selected, the system will perform channel scanning based on the scheduled time set and choose the most suitable channel automatically. |
Output Power | This option enables the configuration of transmission power. |
Client Signal Strength Threshold | This field determines the minimum acceptable client signal strength, specified in decibel-milliwatts (dBm). If client signal strength does not meet this minimum, the client will not be allowed to connect. |
Maximum number of Clients | Enter the maximum clients that can simultaneously connect to your access point or set the value to 0 to allow unlimited clients. |
Discover Nearby Networks | Check this box to enable network discovery. Note that setting Channel to Auto will activate this feature automatically. |
Beacon Rate | This drop-down menu provides the option to send beacons in different transmit bit rates. The bit rates are 1 Mbps, 2 Mbps, 5.5 Mbps, 6 Mbps, and 11 Mbps. |
Beacon Interval | Set the time between each beacon send. Available options are 100 ms, 250 ms, and 500 ms. |
DTIM | Set the frequency for the beacon to include delivery traffic indication messages (DTIM). The interval unit is measured in milliseconds. |
RTS Threshold | Set the minimum packet size for your access point to send an RTS using the RTS/CTS handshake. Setting 0 disables this feature. |
Fragmentation Threshold | Enter a value to limit the maximum frame size, which can improve performance. |
Distance / Time Convertor | This slider and text entry field can be used to interactively set slot time. |
Slot Time | This field provides the option to modify the unit wait time before your access point transmits. The default value is 9μs. |
ACK Timeout | Set the wait time to receive an acknowledgement packet before retransmitting. The default value is 48μs. |
8.2. Status
8.2.1. Access Point
A detailed breakdown of data usage and number of clients for each AP is available at AP > Status > Access Point.
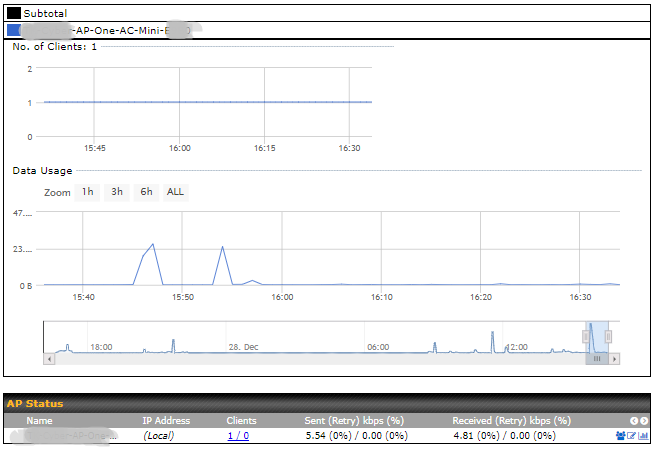
This table shows the detailed information on each AP, including channel, number of clients, power, upload traffic, and download traffic. On the right of the table, you will see the following icons: 
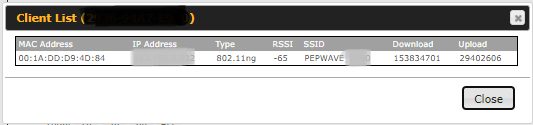
Click the icon to see a usage table for each client:
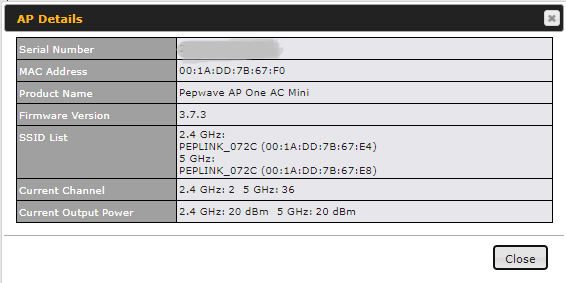
Click the icon to configure AP details.
Click the icon to see a graph displaying usage.
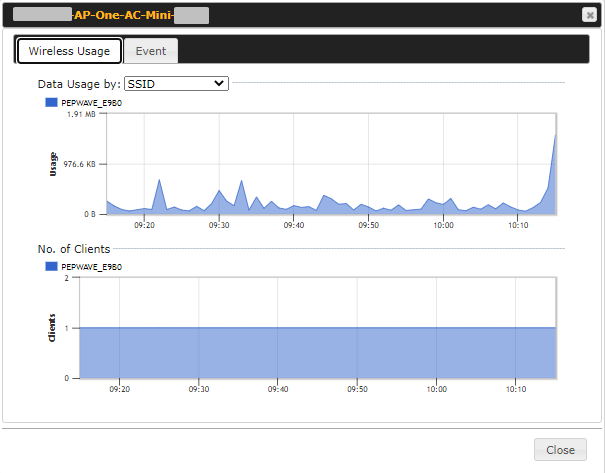
Click any point on the graphs to display detailed usage and client information for that device, using that SSID, at that point in time. On the Data Usage by drop-down menu, you can display the information by SSID or by AP send/receive rate.
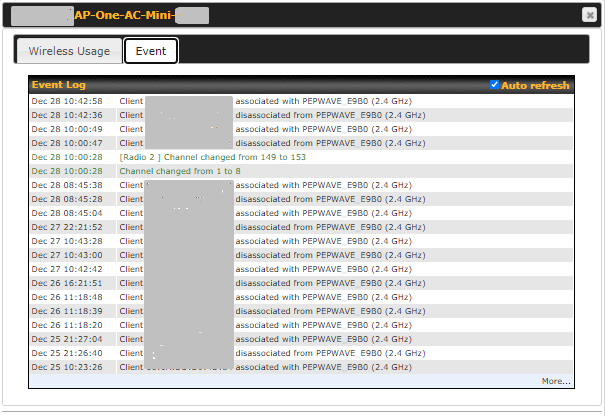
You may click the Event tab which is next to Wireless Usage to view a detailed event log for that particular device.
8.2.2. Wireless SSID
In-depth SSID reports are available under AP > Status > Wireless SSID.
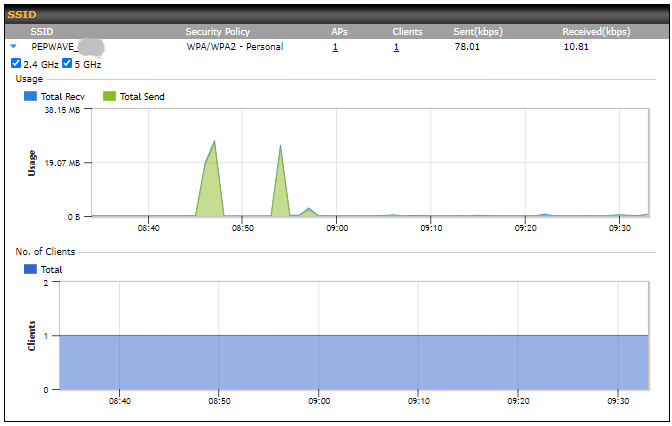
Click the blue arrow on any SSID to obtain more detailed usage information on each SSID.
8.2.3. Wireless Client
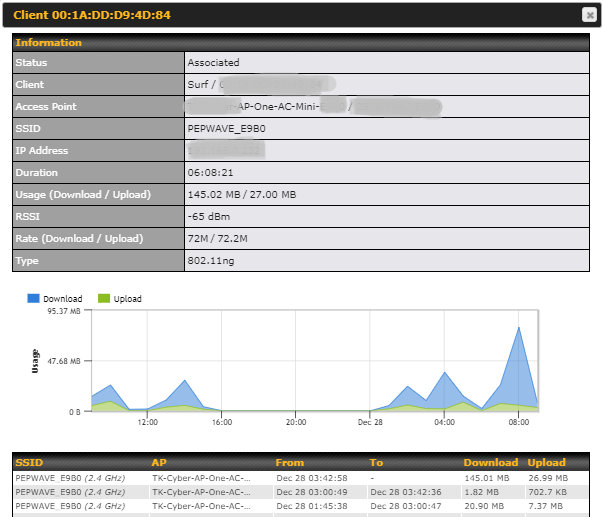
You can search for specific Wi-Fi users by navigating to AP > Status > Wireless Client.
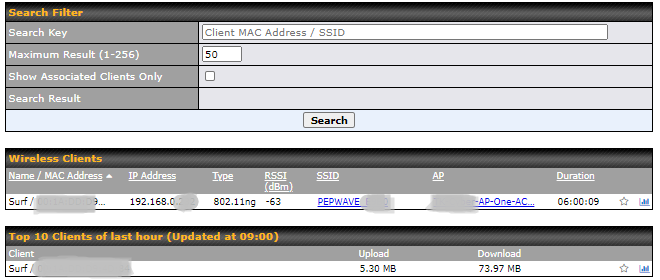
Wireless Client allows you to be able to see your network’s heaviest users as well as search for specific users. Click the icon to bookmark specific users, and click the
 icon for additional details about each user.
8.2.4. Mesh / WDS
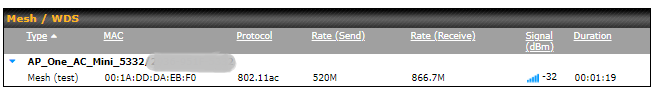
Mesh/WDS allows you to monitor the status of your wireless distribution system (WDS) or Mesh, and track activity by MAC address. This table shows the detailed information of each AP, including protocol, transmit rate (sent / received), signal strength, and duration.
8.2.5. Nearby Device
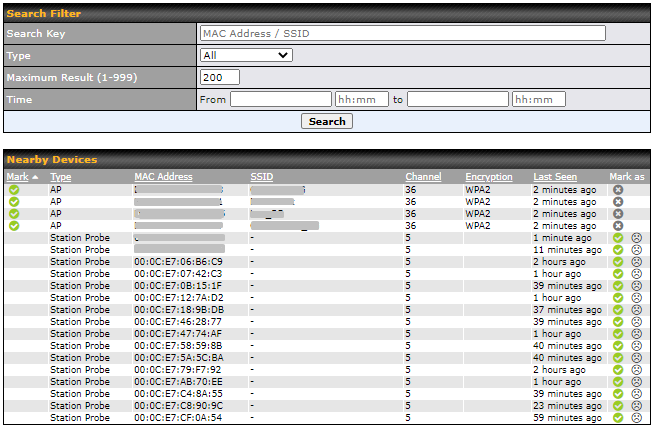
A listing of nearby devices can be accessed by navigating to AP > Status > Nearby Device.
Nearby Devices | |
Hovering over the device MAC address will result in a popup with information on how this device was detected. You may click the |


 icon.
8.2.6. Event Log
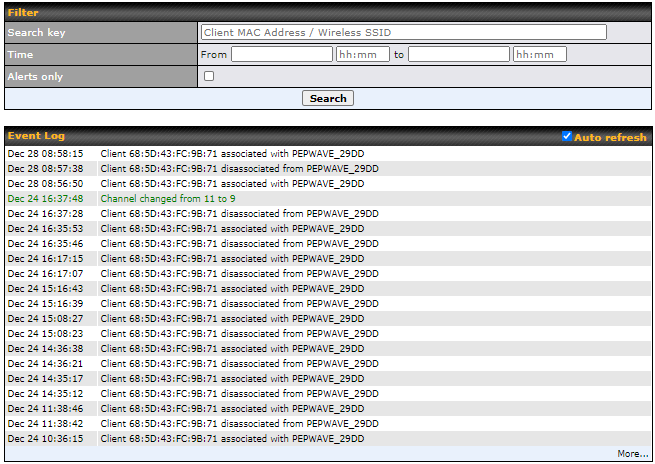
You can access the AP Controller Event log by navigating to AP > Status > Event Log.
Event Log | |
This event log displays all activity on your AP network, down to the client level. You can use the filter box to search by MAC address, SSID, AP Serial Number, or AP Profile name. Click View Alerts to see only alerts, and click the More… link for additional records. |